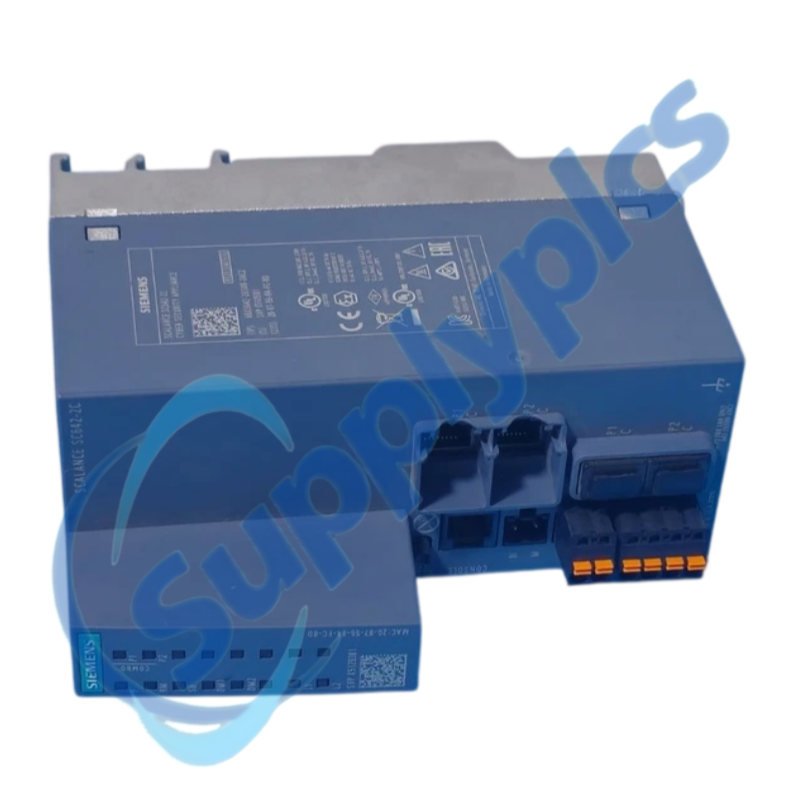
Firewall and secure VPN segmentation for industrial Ethernet cells
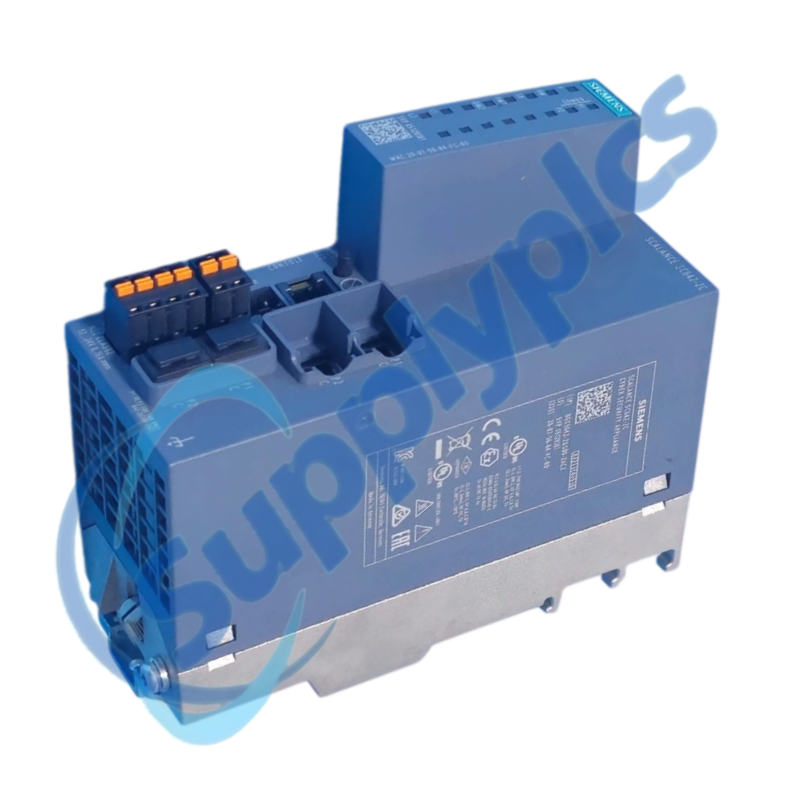
Siemens 6GK5642-2GS00-2AC2 is a SCALANCE S642-2C industrial security appliance providing stateful-inspection firewall, VPN and network-segmentation functions for automation networks.
Verify first: Export the security configuration and verify firmware, certificates, VPN peers, NAT rules, VLANs and network addressing before replacement.
Secure Network Integration
01Export securely
Preserve the approved configuration, certificates and VPN inventory.
02Map every zone
Label trusted, external and redundant paths before moving cables.
03Stage offline
Load firmware and policy in an isolated maintenance network.
04Validate policy
Test required traffic, blocked traffic, VPNs and failover before release.
Specifications
Product type
SCALANCE S642-2C industrial security appliance
Article number
6GK5642-2GS00-2AC2
Security function
Stateful-inspection firewall
VPN protocols
IPsec and OpenVPN
Encryption references
AES, 3DES and DES
Authentication
Pre-shared keys and X.509 certificates
VPN capacity
Up to 200 connections
Network services
NAT and NAPT
Redundancy reference
Standby redundancy
Management reference
SSH, NTP and SNTP
Description
The S642-2C protects industrial cells with stateful packet inspection and supports IPsec or OpenVPN tunnels, certificate-based authentication and network address translation.
Security hardware cannot be exchanged safely from a port map alone. Preserve the approved configuration, keys and certificate chain through the authorized plant-security process, and stage the replacement before connecting it to production.
We review the complete order number and installed-system context before quotation.
Condition coordination
Availability and product condition are confirmed for the requested unit.
Global delivery support
Shipping options and available official documentation are coordinated with the destination.
FAQ
Q1
How should I verify that 6GK5642-2GS00-2AC2 matches the installed system before purchase?
Compare the complete order number, firmware, port role, redundancy design and required firewall/VPN functions. Review the installed security policy and certificates with the authorized network owner before purchasing a replacement.
Q2
What should I back up before replacing 6GK5642-2GS00-2AC2 in a working machine?
Export the approved device configuration through the plant-security process and inventory firewall rules, NAT entries, VPN peers, certificates, keys and management settings. Store the backup in the authorized secured location.
Q3
What should I check if 6GK5642-2GS00-2AC2 powers up but does not become operational?
Keep the device isolated from production while checking both power inputs, port roles and firmware. Review local diagnostics and management access, then load only the validated configuration and certificates.
Q4
How should I troubleshoot a communication or interface problem after installing 6GK5642-2GS00-2AC2?
Verify the trusted and external port mapping, VLANs, routing, NAT rules, peer addresses and certificate validity. Test one permitted service at a time and confirm that blocked traffic remains blocked.
Q5
What should I inspect when 6GK5642-2GS00-2AC2 develops an intermittent fault?
Review interface errors, link negotiation, duplicate addressing, certificate validity, VPN logs, CPU load and redundant-power status. Correlate the event with peer changes or policy deployment before modifying rules.
Q6
Which details should I provide when requesting a quotation for 6GK5642-2GS00-2AC2?
Provide the exact order number, firmware level, network-zone diagram, redundancy requirement and permitted configuration-transfer method. Do not send private keys; coordinate certificate handling through the authorized security owner.

 EN